E-Commerce Checkout Reliability: A Practical Launch Checklist
A clear engineering checklist for secure payments, order states, shipping integrations, duplicate prevention and customer communication.
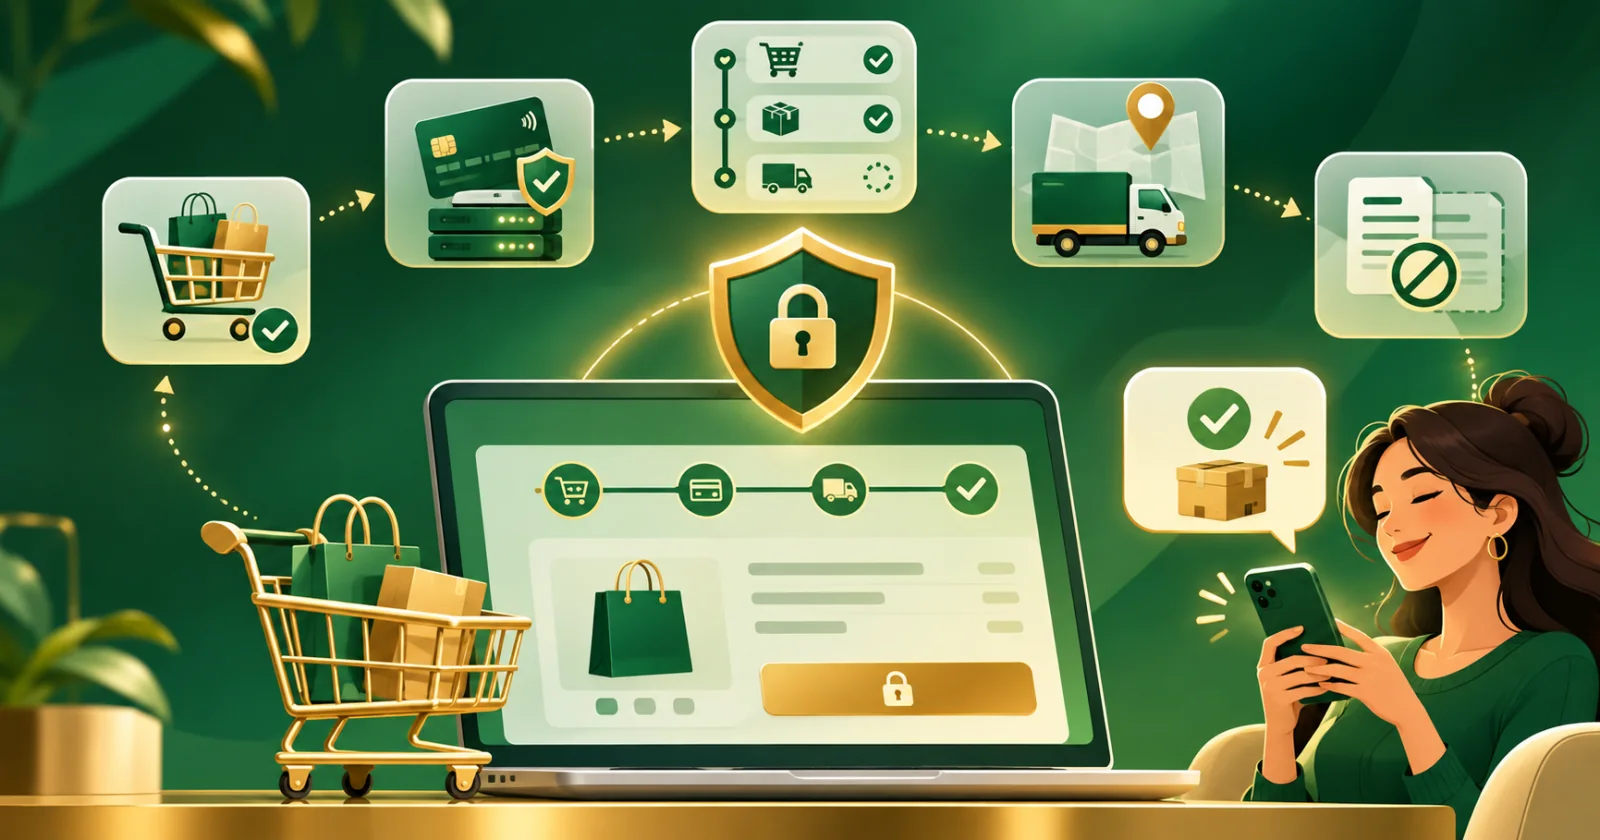
A checkout can look clean and still fail at its most important job: translating a buyer's intent into a valid order and a trustworthy payment state.
Whether a store uses cash on delivery, an online payment gateway or both, the checkout should be predictable for customers and traceable for the business.
1. Define a single source of truth
Do not assume that a redirect to a success page proves payment. The server should verify the transaction through the gateway's trusted callback, verification API or documented reconciliation process.
Keep the customer-facing display separate from the authoritative order state.
2. Design order states carefully
Common states include pending, payment processing, paid, packed, shipped, delivered, cancelled, returned and refunded. The exact model depends on the business.
Write down which transitions are allowed and which actions trigger them. A cancelled order should not accidentally become paid because a delayed callback arrives without validation.
3. Protect against duplicate submission
Users double-click, refresh and retry when a page seems slow. Your system must handle these actions safely.
Use a server-side idempotency key or a well-defined duplicate guard. Check payment references and order identifiers before creating another charge or shipment.
Avoid broad restrictions that block legitimate repeat purchases of different products.
4. Verify every payment notification
Use the gateway's documented validation rules. Confirm transaction identifiers, amounts, currencies, merchant details and permitted status changes.
Do not trust client-provided values for payable totals. Recompute prices, discounts and shipping fees on the server.
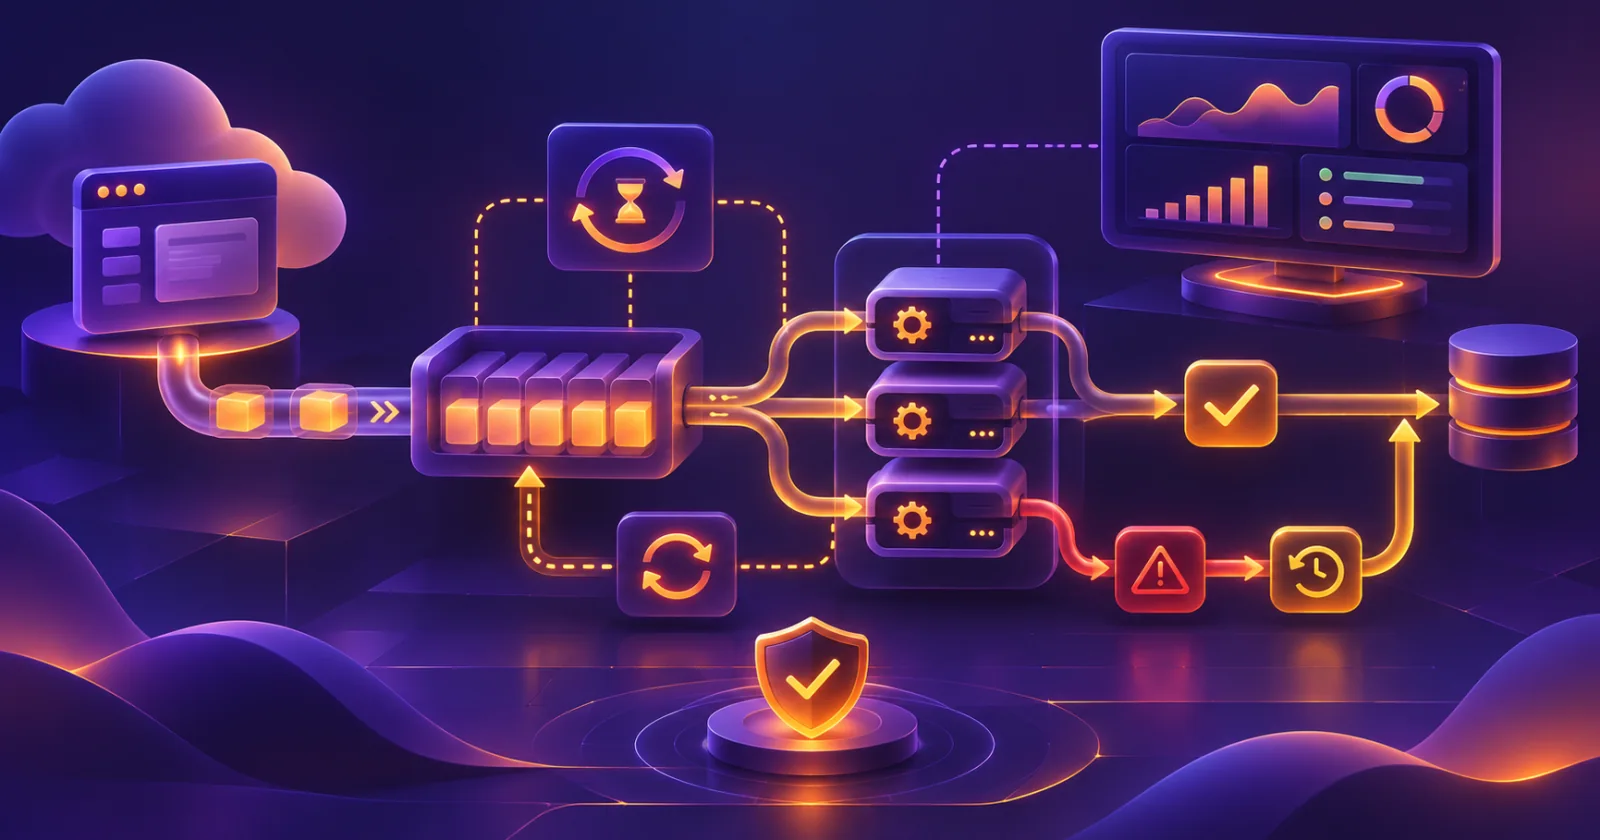
5. Handle asynchronous events
Payment systems and shipping providers may send events out of order or deliver the same event multiple times.
Store the event identifier and processing result. Make each event handler idempotent and preserve an audit trail of significant state changes.
6. Separate payment from fulfillment
Paid does not necessarily mean ready to ship. Check inventory, fraud rules, address quality and business-specific requirements.
Do not create a shipping order more than once just because a webhook was retried.
7. Communicate without overpromising
Customers should see clear next steps: whether payment is pending, the order is confirmed or support is needed.
Send an order confirmation only after the system has recorded the relevant event. Keep communications concise and do not expose full payment details.
8. Test failed and partial journeys
A launch checklist should include:
- Buyer closes the payment popup before finishing.
- Gateway redirects back without a verified payment.
- Browser sends the checkout form twice.
- Payment callback arrives twice or out of order.
- Shipping provider times out after accepting an order.
- A return or cancellation arrives after dispatch.
- Buyer has an active order and attempts a legitimate new purchase.
- An administrator edits an order while a webhook runs.
A happy-path test alone misses the problems that often cost businesses time and money.
9. Keep logs useful and privacy-aware
Record order IDs, state transitions, trusted event IDs and error categories. Avoid placing card details, private access tokens or excessive personal information into logs.
Restrict admin actions and make sensitive changes traceable.
10. Verify live readiness
Before launch, compare sandbox assumptions with production behavior. Confirm credentials, callback URLs, HTTPS, error handling and alerting.
Run a controlled live transaction only when authorized and reconcile it from the buyer view through payment confirmation and the business dashboard.
Final principle
Checkout reliability is about preserving trust through every possible path, not only the successful purchase path.
A store that can explain and recover from incomplete, duplicated and delayed transactions is easier to operate and safer for its customers.
Worked scenario: payment succeeds but the browser never returns
A customer submits checkout, the gateway accepts a payment, and the browser closes before the thank-you screen loads. This is not an edge case to ignore: the order must be determined from authoritative server-side events, not from whether a success page was viewed.
A resilient flow separates three concerns:
- Payment evidence: Verify the provider's notification or documented status-verification mechanism, including authenticity, amount, currency and transaction reference.
- Order transition: Change state only through a permitted transition, with a durable event ID or idempotency key to handle repeat notifications.
- Fulfillment trigger: Create a shipment only once, after payment and business checks are complete. A duplicate callback must not create another shipment.
An incomplete browser redirect should lead the customer to a clearly described pending or recoverable state, not an invented success. If a callback arrives late or out of order, reconcile the events against the provider's authoritative record before changing the order.
A launch-day test plan buyers can verify
Test an end-to-end purchase without relying solely on payment-sandbox success cases.
- Submit checkout twice in rapid succession; confirm there is only one intended payment and order.
- Close the payment window and reopen the order status; verify that the status is truthful.
- Replay the same payment notification; confirm state changes and fulfillment are not duplicated.
- Deliver a delayed event after a cancellation; verify that invalid transitions are rejected or escalated.
- Simulate a shipping-provider timeout after order creation; reconcile before trying again.
- Reconcile gateway settlements, internal paid orders and shipments; document every mismatch.
A professional handoff should include an order-state diagram, callback verification rules, retry policy, reconciliation procedure and a concise customer-support runbook.
Real implementation: a checkout connected to payments and delivery
The [Kinivalo Bangladesh project](/projects/kinivalo-bd/) shows how a custom e-commerce storefront can connect browsing and checkout with payment and fulfillment operations. The documented stack combines PHP, MySQL and JavaScript with bKash payment handling, Cash on Delivery decision rules and Pathao-related order workflows.
The practical engineering challenge is to keep each system's responsibilities clear. A browser submission creates an order request; an authoritative payment event establishes payment status; approved order state allows fulfillment; and customer communication reflects the latest trusted record.
For a store owner evaluating checkout development, these are useful acceptance criteria:
- Accurate order totals: Prices, discounts and delivery charges are calculated on the server.
- Verified payment events: Gateway callbacks and transaction references are checked before updating paid status.
- Duplicate prevention: Repeat form submissions and event notifications are handled without creating unintended extra charges or courier orders.
- Shipping integration: Courier requests use consistent order references, with reconciliation for delayed responses.
- Customer clarity: Order confirmation, pending payment and delivery updates follow the saved order state.
What a business receives from this approach
A custom checkout handoff should include an order-state map, payment verification workflow, fulfillment integration plan, admin review process and end-to-end test checklist. These components are useful for both customer trust and day-to-day store operations. See the [Kinivalo project overview](/projects/kinivalo-bd/) and the OWASP API security guidance.
Further reading and related work
For security and API design principles, see the OWASP REST Security Cheat Sheet and the AWS guidance on idempotent event handling. Explore the [Kinivalo e-commerce project](/projects/kinivalo-bd/) and [development services](/services/) for related project context.
Explore my services and project work, or reach out with your specific challenge.
Discuss a project ↗